What Happens When No One Knows Who Has Your Keys: A Commercial Audit Guide for NCR Facility Managers
There is a particular kind of institutional blind spot that develops slowly, almost politely, inside commercial properties across the National Capital Region. It begins the moment a key is handed to an employee without documentation. It compounds when a contractor returns a badge but keeps a physical copy. It reaches its most dangerous form when a facility manager is asked, point-blank, "Who currently has access to this building?"—and cannot answer.
That question, deceptively simple, sits at the heart of what security professionals call a key audit. And for businesses operating in the NCR—from K Street office suites to Bethesda medical practices to warehouse facilities in Prince George's County—the failure to conduct one annually is not a minor administrative oversight. It is a measurable source of compliance risk, legal exposure, and operational vulnerability.
The Invisible Problem with Commercial Key Distribution
Most commercial properties begin their key management with reasonable intentions. Keys are issued to department heads, maintenance staff, and trusted personnel. A log is kept, at least initially. But organizations grow, staff turns over, and the informal workarounds that feel harmless in the moment—leaving a spare with the front desk, cutting an extra copy for a vendor—accumulate into a system that no longer reflects reality.
By the time a business recognizes the problem, the gap between its official key log and actual key distribution can be substantial. Former employees may still hold working copies. Master keys issued during a renovation two years prior may never have been returned. In multi-tenant commercial buildings, the situation is frequently more complex still, with access layers spanning building management, individual tenants, and third-party service providers.
The NCR's dense concentration of government contractors, healthcare providers, and financial services firms adds another dimension. Many of these organizations operate under regulatory frameworks—HIPAA, FedRAMP adjacent standards, financial industry compliance requirements—that treat physical access control as a component of broader data and asset security. An undocumented key distribution system does not simply create a security gap; it may constitute a compliance deficiency that auditors are specifically trained to identify.
What a Proper Key Audit Actually Involves
A key audit is not a casual walk-through. Conducted properly, it is a structured reconciliation between what your records say and what is physically true. The process generally unfolds across four stages.
Stage One: Inventory Documentation
Begin by pulling every existing record related to physical keys and access credentials. This includes original issuance logs, contractor access agreements, vendor sign-in sheets, and any electronic access control records if your facility uses a hybrid system. The goal at this stage is not accuracy—it is completeness. You need to know what records exist before you can assess their reliability.
Stage Two: Physical Asset Reconciliation
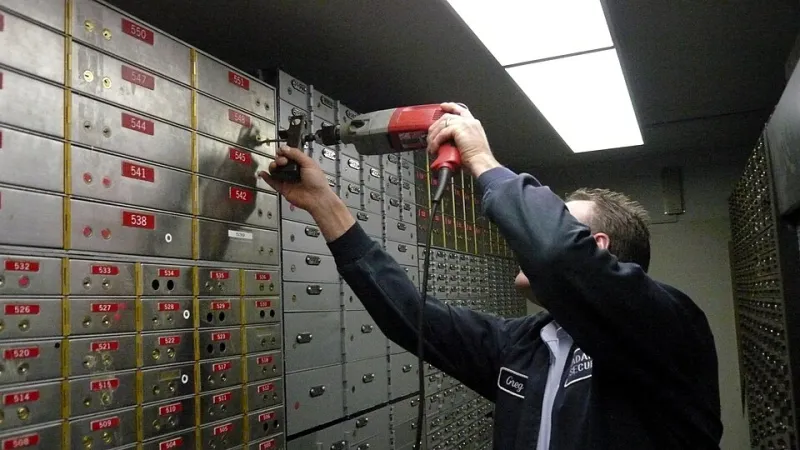
Compare your records against a physical count of every key, lock cylinder, and master key in your system. This means accounting for keys that should be in a key cabinet, keys currently issued to personnel, and keys associated with positions that have since been vacated. Any key that appears in your records but cannot be physically located or confirmed as returned should be flagged immediately.
Stage Three: Personnel Verification
For every key marked as "currently issued," confirm that the named holder is still employed, still requires that level of access, and is aware they hold the key. This step frequently surfaces the most significant discrepancies. Employees who transferred departments, contractors whose engagements ended, and temporary staff brought in for a specific project are common sources of unrecovered keys.
Stage Four: Risk Classification and Remediation
Once discrepancies are identified, they must be ranked by severity. A missing key to a supply closet carries a different risk profile than an unaccounted master key with access to server rooms or executive offices. Remediation actions—rekeying affected cylinders, upgrading specific access points, or transitioning certain areas to electronic access control—should be prioritized accordingly.
The Compliance Dimension NCR Businesses Cannot Ignore
Beyond the operational concerns, there is a regulatory argument for annual audits that many NCR business owners have not fully internalized. Physical access control is increasingly treated as part of a facility's overall security posture in formal compliance assessments. Organizations subject to third-party audits—whether by federal agency partners, insurance carriers, or industry certification bodies—may find that a poorly documented key system creates findings that affect their standing.
Insurance considerations are equally relevant. Commercial property and general liability policies often include language about maintaining reasonable security standards. In the event of a break-in or insider theft, an insurer may scrutinize whether the property owner maintained adequate access control records. A documented annual audit, with corrective actions on file, provides a meaningful layer of protection in those conversations.
Building a Sustainable Audit Schedule
The most effective key audits are not one-time events. They are embedded into a facility's annual operations calendar with the same regularity as fire alarm testing or HVAC maintenance. For NCR businesses, the most practical approach is to tie the audit to a fixed organizational milestone—the start of a fiscal year, the anniversary of a lease renewal, or the conclusion of a major staffing cycle.
Assigning clear ownership is equally important. The audit should have a named responsible party, whether that is a facilities manager, an office administrator, or a designated security coordinator. Without accountability, even a well-designed audit process tends to drift.
For larger commercial properties or organizations with complex access hierarchies, working with a licensed locksmith service familiar with the NCR market can add significant value. Professionals in this space can assess whether existing lock hardware meets current standards, recommend cylinder upgrades where appropriate, and provide documentation that supports compliance reporting.
When the Audit Reveals More Than Expected
It is worth preparing for the possibility that your first formal audit will surface more discrepancies than anticipated. This is not unusual, particularly for organizations that have never conducted a structured review. The appropriate response is not alarm but systematic remediation.
In practice, this often means rekeying a portion of the facility rather than replacing hardware outright—a cost-effective approach that immediately neutralizes the risk posed by unrecovered keys without requiring a full lock replacement. From there, implementing a more rigorous issuance and return protocol ensures that the next audit begins from a cleaner baseline.
The goal, ultimately, is not a perfect system—it is a documented, defensible one. In a region where commercial real estate, regulatory scrutiny, and physical security concerns intersect as they do across the NCR, the businesses that treat key management as a serious operational discipline are the ones best positioned to avoid the incidents that make it unavoidable.
If your organization has not conducted a formal key audit in the past twelve months, the time to schedule one is now—before a missing key becomes a missing answer when it matters most.